Payment integration
Connect payment providers and internal applications with clear transaction states, retries, and duplicate handling.
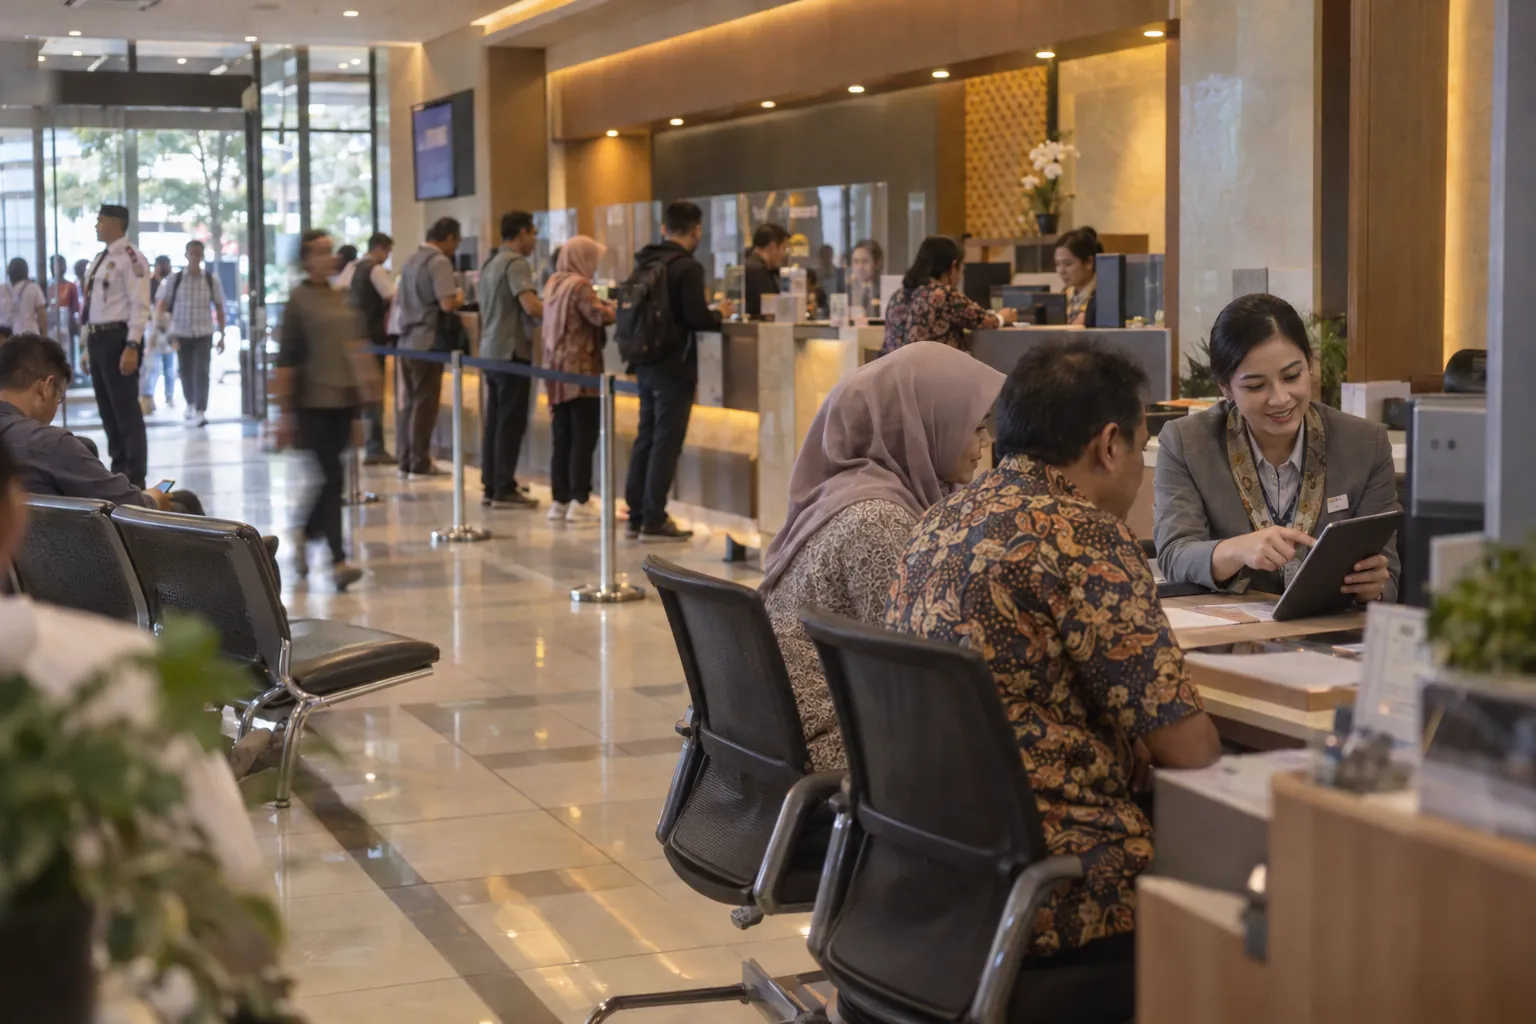
BANKING & FINANCIAL SERVICES
Build and modernize financial platforms with connected payment systems, reliable data flows, and controlled access. Teknalogi translates complex operational requirements into systems that are ready to operate and evolve.
Discuss your requirements
Financial operations become difficult to manage when customer, payment, and internal systems operate independently.
Customer, transaction, and reporting data becomes difficult to keep consistent across platforms.
Teams spend time matching records and investigating incomplete or inconsistent transactions.
Fragmented logs and delayed reporting slow down service issue investigations.
New products and integrations add requirements for approvals, data access, and audit records.
Discovery defines the scope so architecture, integrations, and workflows fit the systems already in operation.
Connect payment providers and internal applications with clear transaction states, retries, and duplicate handling.
Support account services, document submission, application tracking, and partner interactions with controlled access.
Bring transaction records, matching rules, exception queues, and settlement reporting into one operational view.
Coordinate forms, documents, verification providers, internal reviews, and approval history.
Build approvals, case management, operational reporting, and back-office administration.
Connect established systems to new applications through documented interfaces and phased releases.
Define transaction states, validation, idempotency, and the event records needed for investigation and change review.
Align permissions with operational roles, then plan how sensitive data is collected, transmitted, stored, masked, and removed.
Test failure handling, backup restoration, monitoring, and deployment procedures against agreed service targets.
Modern banking demands rapid feature delivery and flexible integrations without compromising the stability of core ledger systems. Many financial institutions face bottlenecks where legacy monolithic architectures cannot efficiently communicate with modern digital touchpoints.
Teknalogi engineers integration middleware and event-driven microservices orchestration. This pattern isolates heavy read traffic from core transaction databases, keeping customer applications highly responsive during peak hours.
Through disciplined dependency separation, financial institutions can launch new savings, credit, and partner products with significantly accelerated development cycles.
Interbank fund transfers require deterministic transaction states and resilience against third-party network interruptions.
We build payment processing pipelines featuring strict idempotency, asynchronous message queues with adaptive retry policies, and automated multi-channel reconciliation.
Robust payment processing pipelines safeguard financial balance sheets and eliminate costly manual dispute investigations.
Security in banking is the bedrock of public trust and business continuity. Every interaction endpoint requires defense-in-depth protection against sophisticated cyber threats.
Our implementation includes end-to-end data encryption (E2EE), cryptographic payload signing with timestamp verification, and proactive traffic anomaly monitoring.
Security controls are engineered to run transparently, preserving a frictionless customer experience during legitimate transactions.
Compliance with personal data protection regulations requires strict data segregation and selective access governance over financial records.
We implement isolated data architectures where Personally Identifiable Information (PII) and account credentials are encrypted both in transit and at rest.
Structured data governance guarantees customer privacy and regulatory adherence throughout the data lifecycle.
Maintaining 24/7 financial service availability requires software designed to absorb infrastructure hiccups without cascading failures.
Our systems incorporate multi-zone redundancy, intelligent circuit breakers, and dead-letter queues (DLQ) so external provider downtime never brings down core platform capabilities.
Resilient software design gives operational peace of mind to leadership and seamless reliability to end users.
Every financial movement, configuration change, and administrative action must remain verifiable for internal governance and regulatory scrutiny.
We incorporate append-only immutable audit logging and dual-control maker-checker approval workflows for critical platform actions.
Rigorous audit trails keep financial institutions continually prepared for external inspections and risk assessments.
Integration and control requirements vary between organizations. Discovery helps define system boundaries, risks, and the implementation scope.
Integration feasibility depends on available APIs, documentation, access restrictions, and system dependencies. We review these during discovery before defining the integration approach.
Multiple providers can be considered in the architecture. The scope needs to handle differences in authentication, transaction states, callbacks, refunds, and reconciliation formats.
We define data handling and access requirements with your team. Implementation may include encryption, role-based permissions, secrets management, and masking of sensitive information in logs.
A phased approach may work when system dependencies, data consistency requirements, and deployment windows support it. The migration plan is defined after the current environment is mapped.
No. Technical controls, documentation, assessment support, and compliance responsibilities must be agreed with your risk and compliance teams as part of the project scope.
We map system dependencies, transaction flows, operational roles, access boundaries, and exception scenarios. The output informs the architecture, delivery scope, and acceptance criteria.
Test scenarios can cover timeouts, repeated callbacks, interrupted processing, reversals, and reconciliation differences. The exact cases depend on the transaction model and provider behavior.
Post-launch support can include monitoring, issue investigation, maintenance, and further development. Support hours, response expectations, and responsibilities are agreed separately.

We're ready to help you deliver high-performing websites, boost your business visibility in search engines, and build digital platforms tailored to your specific needs.